How Agentic AI Payments Work: Signed Mandates, Scoped Tokens and Chargeback Risk
Oct. 15, 2026 • Deep Dive • AI in Fintech
AI agents can select products and initiate payments without a buyer present at checkout, forcing merchants and payment providers to verify delegated authority rather than a single approval. Google’s Agent Payments Protocol (AP2) uses signed mandates to record spending limits and connect instructions to a specific cart. Stripe and OpenAI’s Agentic Commerce Protocol and Shared Payment Tokens, alongside Mastercard’s Agentic Token framework, support checkout with restricted credentials. Visa’s Trusted Agent Protocol helps merchants identify agents, while Coinbase’s x402 enables stablecoin payments through web requests, including small API charges.
These tools address different risks: signatures document permission, tokens limit payment use, and records can support disputes. But compliance with a spending cap cannot prove an agent chose what its user intended. Google transferred AP2 stewardship to the FIDO Alliance in April 2026, yet consumer deployment remains early. Merchants still face integration challenges, while liability and chargeback treatment for agent errors remain unsettled.
An AI agent can compare options, assemble a cart and initiate payment before its user sees a checkout page. That changes more than the interface. Conventional online payments typically ask whether a person approved a particular transaction. Agentic AI payments must establish something harder: whether software was authorized to act, whether a purchase stayed within that authority and who bears the cost if it did not.
The emerging answer combines signed instructions, tightly restricted payment credentials and records linking the two. Google’s Agent Payments Protocol (AP2), Stripe and OpenAI’s Agentic Commerce Protocol (ACP), and initiatives from Visa and Mastercard approach different parts of that problem. A separate model, x402, puts stablecoin payments into web requests. None removes the central difficulty: proving what an agent was permitted to do is not always the same as proving it made the right decision.
From checkout approval to delegated authority
Online commerce developed around interactive steps such as card security codes, multi-factor authentication, 3D Secure and device biometrics. Those steps fit a buyer who can be asked to approve a purchase at checkout. An autonomous agent may instead receive instructions earlier, then transact later without seeking approval for each order.
The instruction might permit purchases up to a ceiling, from certain types of merchants and before a specified expiry. The payment system then needs to carry those limits through product selection, checkout and settlement. Otherwise, a merchant can see that an agent has a way to pay but cannot reliably establish what its principal authorized.
Standards activity accelerated in 2025. Cloudflare proposed Web Bot Auth for cryptographically identifying automated traffic, while Coinbase introduced x402 for payments through HTTP requests. Google announced AP2 in September; Stripe and OpenAI introduced ACP and a Shared Payment Token mechanism. Visa followed with its Trusted Agent Protocol (TAP), and Mastercard introduced its Agentic Token framework.
In April 2026, Google transferred AP2 stewardship to the FIDO Alliance and published version 0.2, specifying autonomous flows in which the human is not present at checkout. These are significant steps toward shared infrastructure, but a published specification is not evidence that agent checkout is routine across merchants. The research describes consumer-facing deployment as an early transition, with integration hurdles around initial checkout pilots.
What a signed mandate actually proves
A mandate is a machine-readable record of delegated authority. In the AP2 model, an Intent Mandate can express the principal’s purchasing conditions, including spending caps, permitted categories and an expiration time. A digital signature, potentially anchored in a passkey or verifiable credential, lets a verifier check that the record is tied to the relevant signing authority and has not been altered.
The agent then chooses items and produces a Cart Mandate connecting the proposed purchase to the earlier instruction. That second record can bind line items, shipping details and a final price to the original authorization. In principle, the merchant or payment provider can examine a chain from principal to agent to specific cart, rather than rely on an assertion that the agent had permission.
Consider an agent instructed to restock inventory within a defined budget. A signed spending limit provides a testable boundary; a cart priced above it should fail that test. The signature does not, by itself, establish that the selected goods were suitable. That distinction matters when instructions are broad or the agent’s interpretation is wrong.
There is also an operational security problem. The private keys used to delegate or exercise authority must be protected. The research identifies cloud-hosted agent environments as targets for key theft, prompt injection and mandate hijacking. Cryptography can make an instruction verifiable, but compromised signing authority can still produce apparently valid instructions. The value of an audit trail therefore depends on the security of the system that creates it.
Why payment credentials need their own limits
A mandate describes permission; a payment token controls how a credential can be used. Instead of giving an agent a reusable card number, a payment service provider or token service can issue a credential restricted to one merchant, a maximum amount and a short validity period. Stripe’s Shared Payment Token and Mastercard’s Agentic Token framework illustrate this approach.
Those restrictions narrow the potential damage if a token leaks or an agent attempts a purchase outside its assigned task. They also give the merchant a concrete payment artifact tied to the proposed cart. But a token is not a substitute for the mandate. A successful charge within its amount ceiling shows that the payment complied with the token’s technical limits, not necessarily that the underlying choice matched the principal’s intentions.
A further check may happen before checkout. Through TAP or Cloudflare’s Web Bot Auth, an agent can sign an HTTP request so a merchant or edge service can verify its identity against a trusted public key. That helps distinguish an authenticated purchasing agent from other automated traffic. It answers who is making the request, however, not whether every requested purchase is authorized. Identity verification, delegated authority and payment control are related checks with different purposes.
ACP offers one route for integrating these controls into commerce. Stripe and OpenAI developed it alongside Shared Payment Tokens for checkout within ChatGPT. The broader challenge is merchant participation: agents need ways to discover products and complete transactions that merchants will accept, while merchants need enough evidence to trust requests made without a human browser session.
Card rails and machine-native payments
Much of agentic commerce extends existing card infrastructure. Mandates and agent identity checks add context around a transaction; scoped tokens keep reusable card credentials out of the agent’s hands; established payment rails handle processing. Visa, Mastercard and Stripe are all developing components for this path.
The alternative highlighted by x402 uses the web’s Payment Required response to request payment for a resource. Client software can respond by transmitting a stablecoin payment with its HTTP request, making it possible to charge for individual API calls, database queries or compute access. Coinbase introduced the protocol, and the Linux Foundation launched the x402 Foundation in July 2026 with founding members drawn from card networks, technology companies and payment providers.
The x402 Foundation reported 75.41 million transactions totaling $24.24 million over one 30-day monitoring window in mid-2026, an average of $0.32 each. That illustrates the small-payment use case. It does not establish that stablecoins will displace cards for consumer shopping. A paid API request and a disputed retail purchase involve different merchant relationships, customer expectations and remedies.
Investment is also moving toward infrastructure for autonomous buyers. Finextra reported that Natural raised $30 million in a July 2026 Series A to build agent coordination and dedicated banking rails. Funding and protocol activity show commercial interest, but neither resolves which architecture merchants will adopt at scale.
The chargeback dilemma: evidence without a human session
Card disputes often draw on evidence from a human checkout: device information, location signals and behavior during a shopping session. An agent may leave little comparable human-session evidence at the moment of purchase. A merchant contesting a chargeback might instead submit the signed mandate, the cart record, execution logs and token restrictions.
That record could be powerful when the dispute is about whether authority was granted or whether a stated limit was exceeded. It is less conclusive when an agent stays within a numerical limit but misunderstands a request. A non-refundable booking could meet loosely specified criteria yet still be something the customer says they never intended to buy. A cryptographic signature cannot determine whether the agent exercised good judgment.
The scale of existing dispute operations makes this more than a hypothetical process question. Visa reported processing 106 million card disputes in 2025. That figure describes overall card disputes, not agentic-payment disputes, but it indicates the system into which autonomous purchases may arrive.
There is no agreed answer on who should pay when an authorized agent makes a costly mistake. In a survey of 500 senior fraud, risk and security professionals cited in the research, 39% assigned liability to the AI agent provider, 20% to the customer, 15% favored shared liability, 14% named the merchant and 11% the bank or processor. Those responses are views, not binding rules. The research also identifies uncertainty over how existing consumer-protection and dispute frameworks apply when an agent acts outside the user’s intended scope.
What has to come together
The technical pieces answer distinct questions. An agent signature identifies automated traffic. A signed mandate records delegated boundaries. A scoped token constrains payment execution. Cart records and logs connect those steps for later review. Used together, they could give merchants and payment providers better evidence than a payment credential alone.
The remaining gaps are as much institutional as technical. Merchants must decide which agent requests and checkout specifications to support; standards bodies must make credentials and mandates interoperable; dispute systems must determine how much weight to give machine-generated evidence. Card rails and x402 address different payment needs, and the research does not establish that either will become the dominant model.
Agentic payments are therefore best understood as a shift from approving each checkout to governing a delegated process. Cryptography and scoped tokens can make that process more controlled and inspectable. They cannot, on their own, decide whether a plausible purchase was the purchase a human meant to authorize.
The Linux Foundation appointed payments veteran Michael Hursta executive director of the x402 Foundation on October 1, 2026, as payment systems designed for autonomous AI agents gained attention. Foundation members reported more than 75 million agentic payment transactions in a 30-day period in September, and Coinbase and Amazon Web Services showcased production payment rails at Sibos 2026. Reported transaction counts, however, do not establish the value or commercial character of that activity. The emerging protocols address different obstacles. Coinbase’s x402 enables per-request USDC payments through HTTP, while Google’s Agent Payments Protocol uses signed mandates to connect an agent’s purchases to a user’s authorization. Stripe and Tempo have also proposed session-based billing through the Machine Payments Protocol. These approaches respond to card fees and interactive checkout checks that can impede small, automated transactions. Card networks are developing delegated-identity tools, leaving multiple potential paths for agent payments rather than a single replacement for existing rails.
Mastercard opened developer early access for Agent Pay for Machines (AP4M) on October 20, 2026, releasing buyer- and seller-side APIs, a sandbox and developer toolkits. In a Cloudflare Connect demonstration, marketing agency Hype tested an autonomous agent making nine payments to two merchants within a single budget, without manual billing or account setup. AP4M uses HTTP 402 payment challenges, but differs from crypto-native implementations of the x402 protocol. Its agents issue digitally signed vouchers off-chain; merchants can batch and redeem them later instead of settling every request on-chain. The pilot combined agent wallet infrastructure from Coinbase Developer Platform and BVNK, settlement on Base, and Mastercard’s multi-currency fiat and stablecoin settlement platform. Circle separately expanded its managed payments service to target AI-agent traffic using USDC. Together, the developments show competing approaches to machine-to-machine payments, with different choices about settlement, funding and who manages digital assets.
Visa launched a live pilot with BILL and Billtrust at Money20/20 USA in late October 2026 to test end-to-end B2B invoice payments executed by software agents. The agents act on invoices enterprise buyers have already approved; they do not decide which supplier payments to authorize. Visa’s Trusted Agent Protocol and Agentic Directory are designed to authenticate those agents when they access supplier and merchant portals without shared credentials or manual human login. Separately, Visa has put Commercial Payment Controls into production for eligible issuers in supported regions, allowing businesses to set limits and restrictions on corporate spending. The company plans general availability of Commercial Virtual Authentication and Commercial Supplier Validation in 2027 after pilot completion. Its SESA 2.0 analytics platform has identified more than $600 billion in potentially cardable supplier spend. The pilot tests whether approved invoice payments can be executed through automated workflows while preserving buyer-defined controls.
Mastercard and Visa are advancing different approaches to AI-initiated business payments. At Cloudflare Connect, Mastercard demonstrated an agent making nine payments across multiple service providers under one authorized budget. It also opened early developer access to Agent Pay APIs, a sandbox and toolkits. Visa expanded its commercial agentic suite around a BILL and Billtrust pilot, alongside spend analytics and fraud tools. The distinction is how each approach constrains the agent. Visa’s pilot lets an agent pay invoices that buyers have already approved, using its Trusted Agent Protocol to navigate supplier-portal security without sharing underlying login credentials. Mastercard is testing controls for machine-to-machine transactions, including signed vouchers, agent verification and a score intended to estimate whether an incoming transaction was AI-initiated. Both efforts leave a consequential question for business payments: how responsibility should be assigned when an authorized agent follows its technical instructions but breaches a procurement condition.
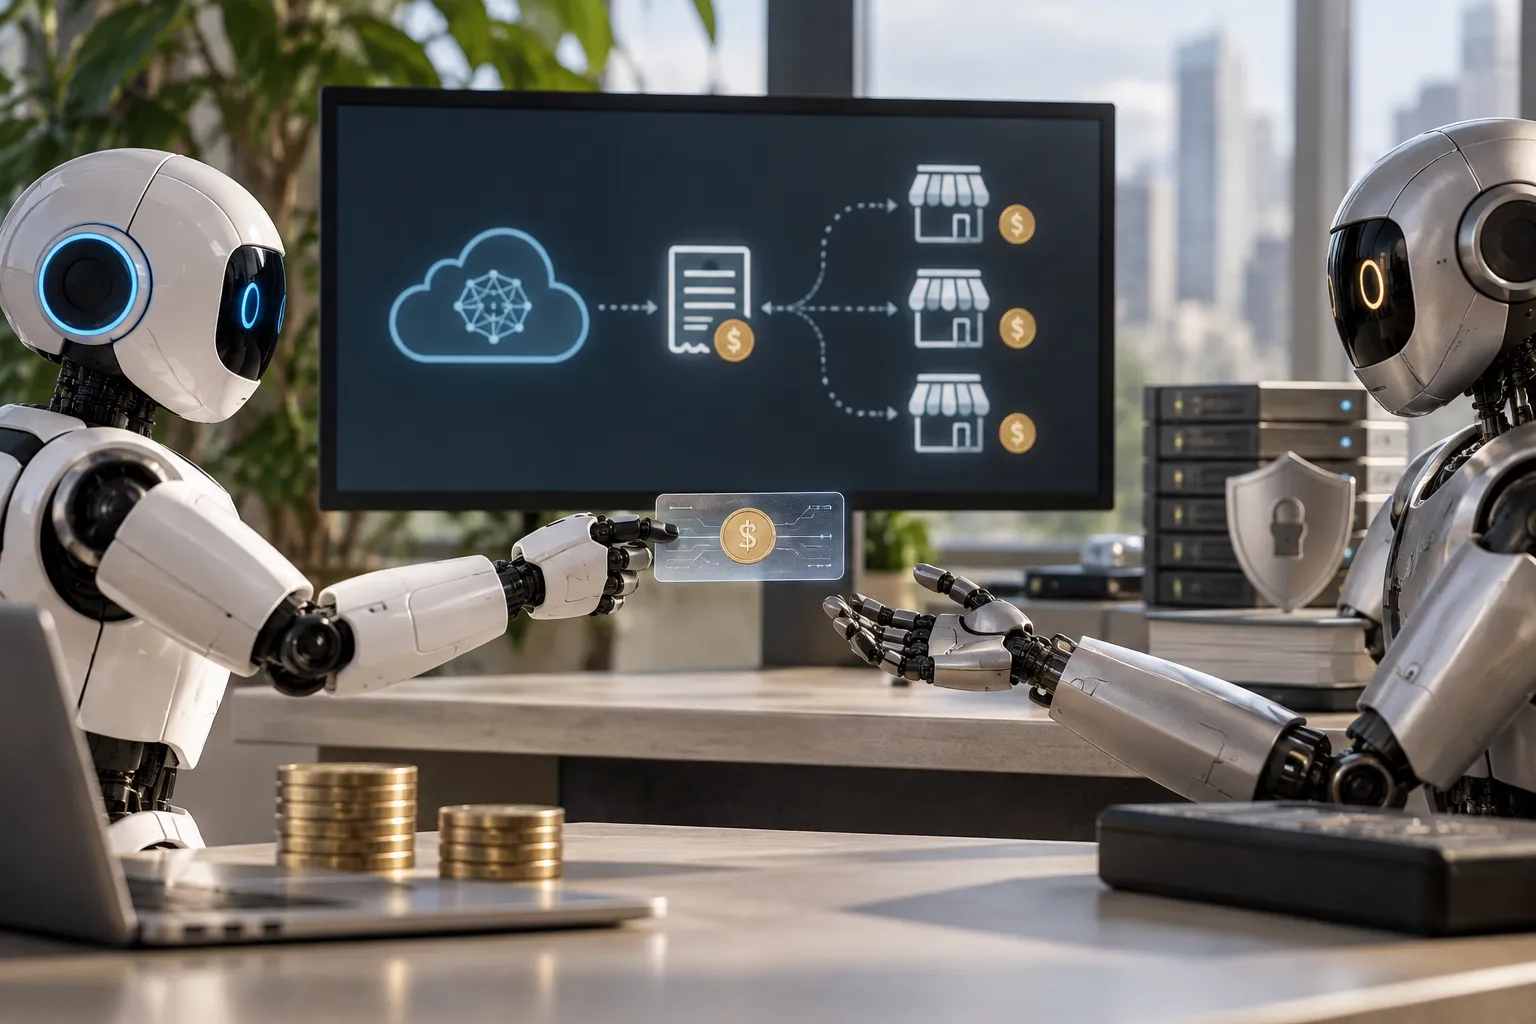
Mastercard opened developer APIs, SDKs and a sandbox for Agent Pay for Machines (AP4M) on October 21, 2026. The tools enable autonomous AI agents on Amazon Bedrock to make multi-merchant micropayments over x402 using off-chain signed vouchers. The launch follows Coinbase Developer Platform’s report that cumulative x402 payments across Base and Solana had exceeded 100 million by October. The x402 protocol uses an HTTP 402 response to tell an agent what a service costs and how to pay. Its growing infrastructure includes a Linux Foundation-governed foundation, while alternative approaches use Lightning payments or existing processor rails. Transaction counts, however, do not establish how much genuine agent-led commerce is taking place. TRM Labs found a much smaller pool of plausible commercial trade after screening out other activity. Security questions also remain, including whether a service can receive payment without delivering its output. Developers therefore face choices about settlement, spending controls and proof of service.
CapitalOS completed a $21.9 million Series A financing round on October 21, 2026, led by LGVP. The company plans to expand its engineering team and scale the infrastructure behind its AI-driven money orchestration platform. WEX Venture Capital, Group 11, Great North Ventures, Night Capital and existing early investors also participated. Founded in 2022, CapitalOS helps vertical SaaS and AI platforms offer embedded charge cards, digital wallets and automated bill payments without maintaining in-house licensing or risk operations. Its architecture uses five specialized AI agents across underwriting, capital, compliance, risk and fraud, and support. Property management platform Guesty is an active customer, and CapitalOS reports managing transactions for more than 25,000 active cardholders across dozens of integrated platforms. CapitalOS relies on infrastructure provider Increase and its chartered partner banks rather than replacing depository institutions. The announcement did not disclose a valuation, credit warehouse partner or the identities of its current primary sponsor banks.